
Chapter 15 · 15.9
Password Protected Directories
Do you want to shield part of your website, for example a test version, a folder with documents for clients or an admin page? Then put a password on it. Visitors will then first see a browser login window. You do this under Password Protected Directories, under Advanced Features.
Protecting a directory
- Choose the correct domain at the top right (see Working with multiple domains: the domain selector).
- Click Password Protected Directories under Advanced Features. You'll see the protected directories for this domain.
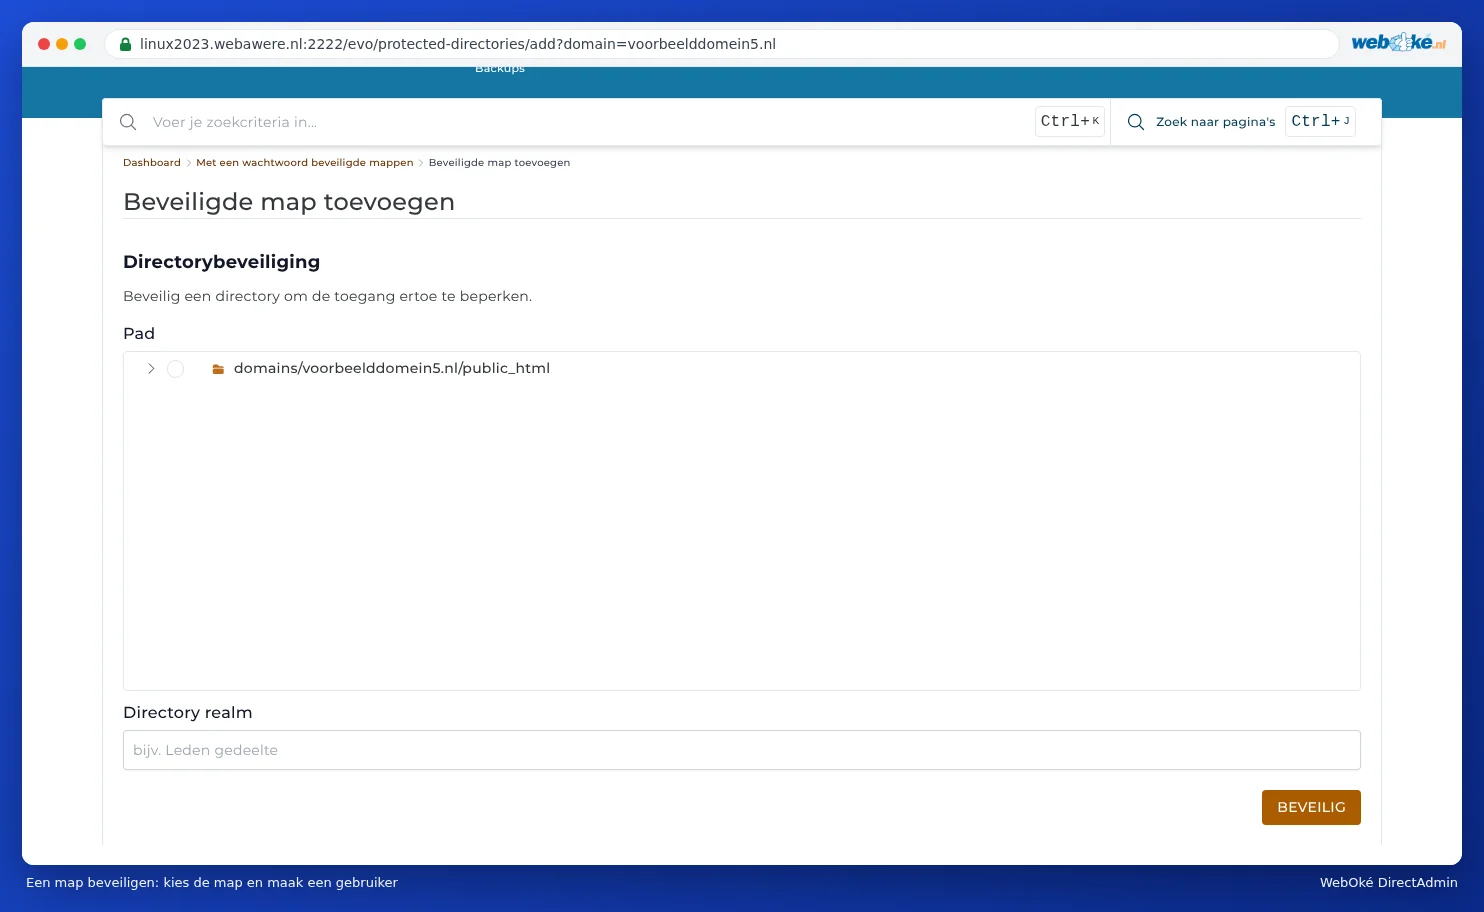
- Click ADD PROTECTED DIRECTORY (1).
- Under Path, choose the directory you want to protect from the directory list. The list starts at domains/yourdomain.com/public_html.
- Under Directory realm, enter the text that will appear in the login window, for example "Clients only".
- Click PROTECT.
- Then add the users who are allowed into the directory, each with their own username and password.

Then open the directory in a private window of your browser. You'll now need to log in first. The protection also applies to all directories and files underneath it.
Good to know
- Only use this on a site with https (see What is SSL and how does WebOké arrange it?). Without https, the password travels across the internet in readable form.
- These are separate users, only for this directory. They have nothing to do with your DA password or with WordPress users.
- DirectAdmin puts the protection in a .htaccess file in the directory. If you edit that .htaccess yourself, leave the lines with Auth in place.
- Do you want to protect a single WordPress file, such as wp-login.php? Then a protected directory isn't the right approach. Use a security plugin or two-step login in WordPress for that instead.
Removing protection
Click the directory in the list and switch off the protection, or remove the directory from the list. Do you get a 500 error afterwards, or does the login window keep appearing? Then check the .htaccess file of that directory (see Showing and editing hidden files such as .htaccess) for any remaining lines with AuthType, AuthName, AuthUserFile or require valid-user, and remove them.